Resources · Guide
Connect a Streamable HTTP server.
Add the MCP servers your agents should reach. Meandr holds the credentials and signs each call, so your agents only ever hold a Meandr token.
Three steps
From server URL to curated tools.
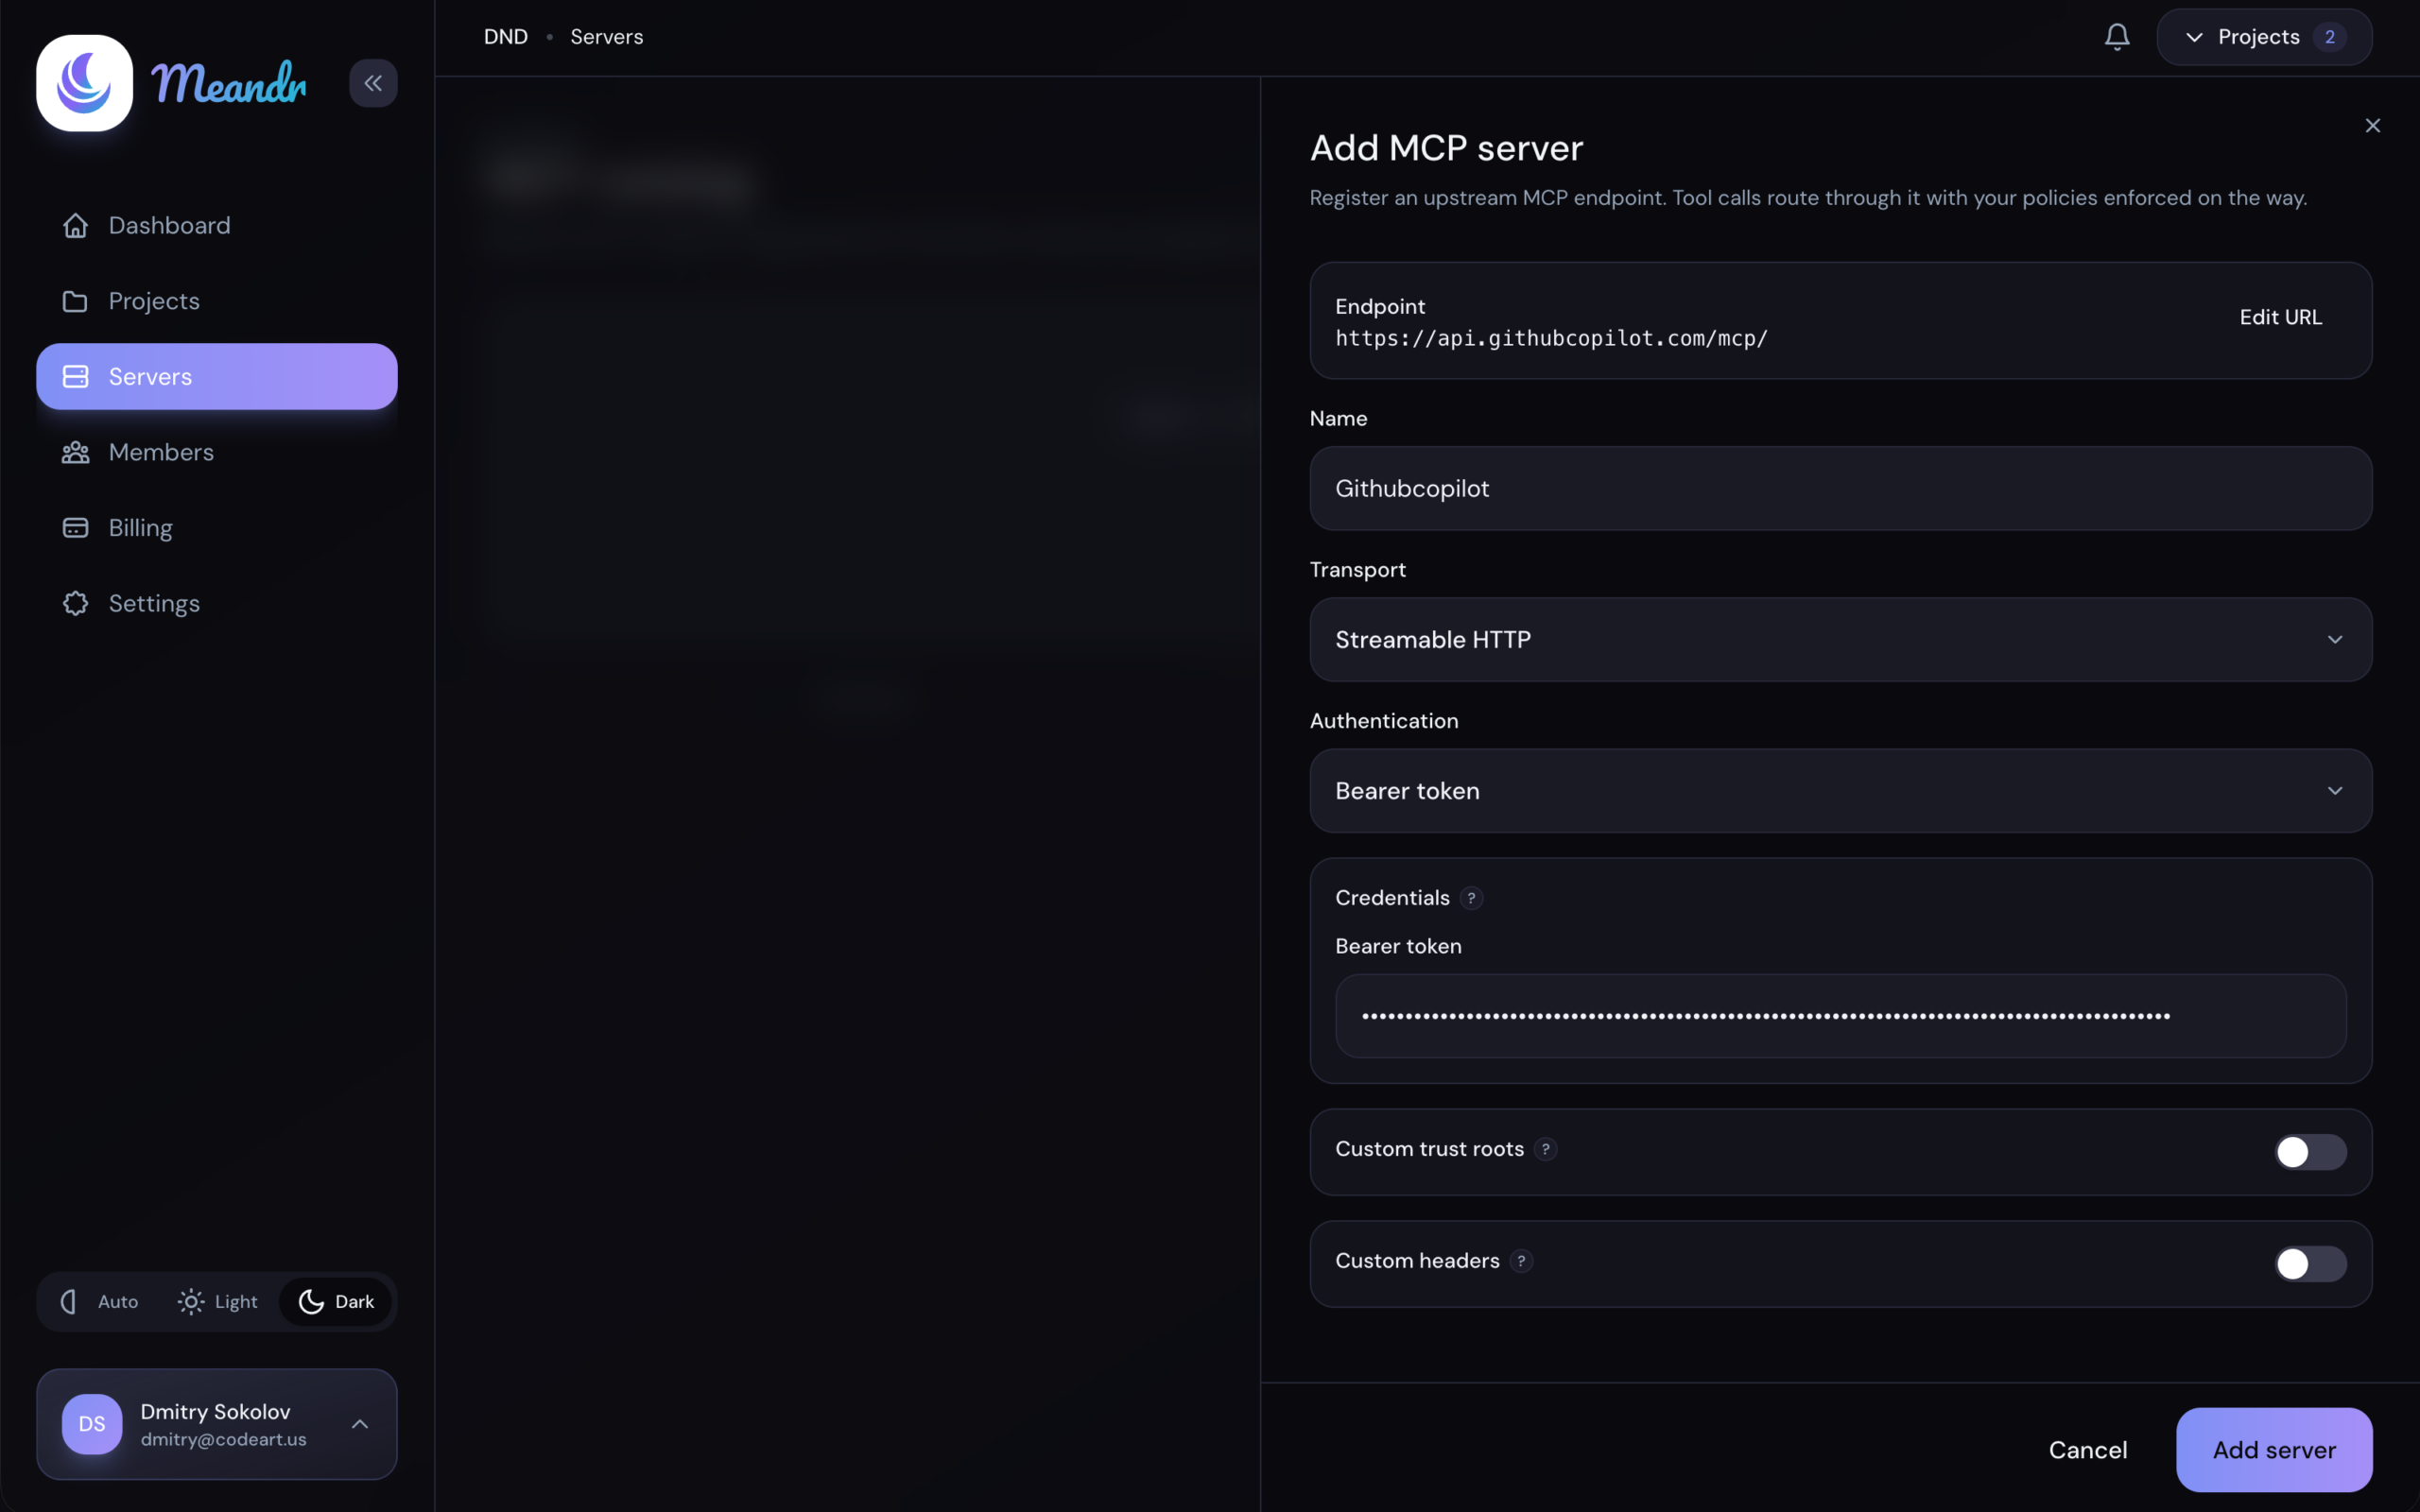
Add the server
URL and auth.
Give Meandr the server's URL and how it authenticates. Meandr stores the credentials encrypted and uses them only to sign requests to that server.
Meandr checks it
Reach and sign-in.
Meandr verifies it can reach the server and sign in before the server goes live in your catalog — nothing broken gets exposed to an agent.
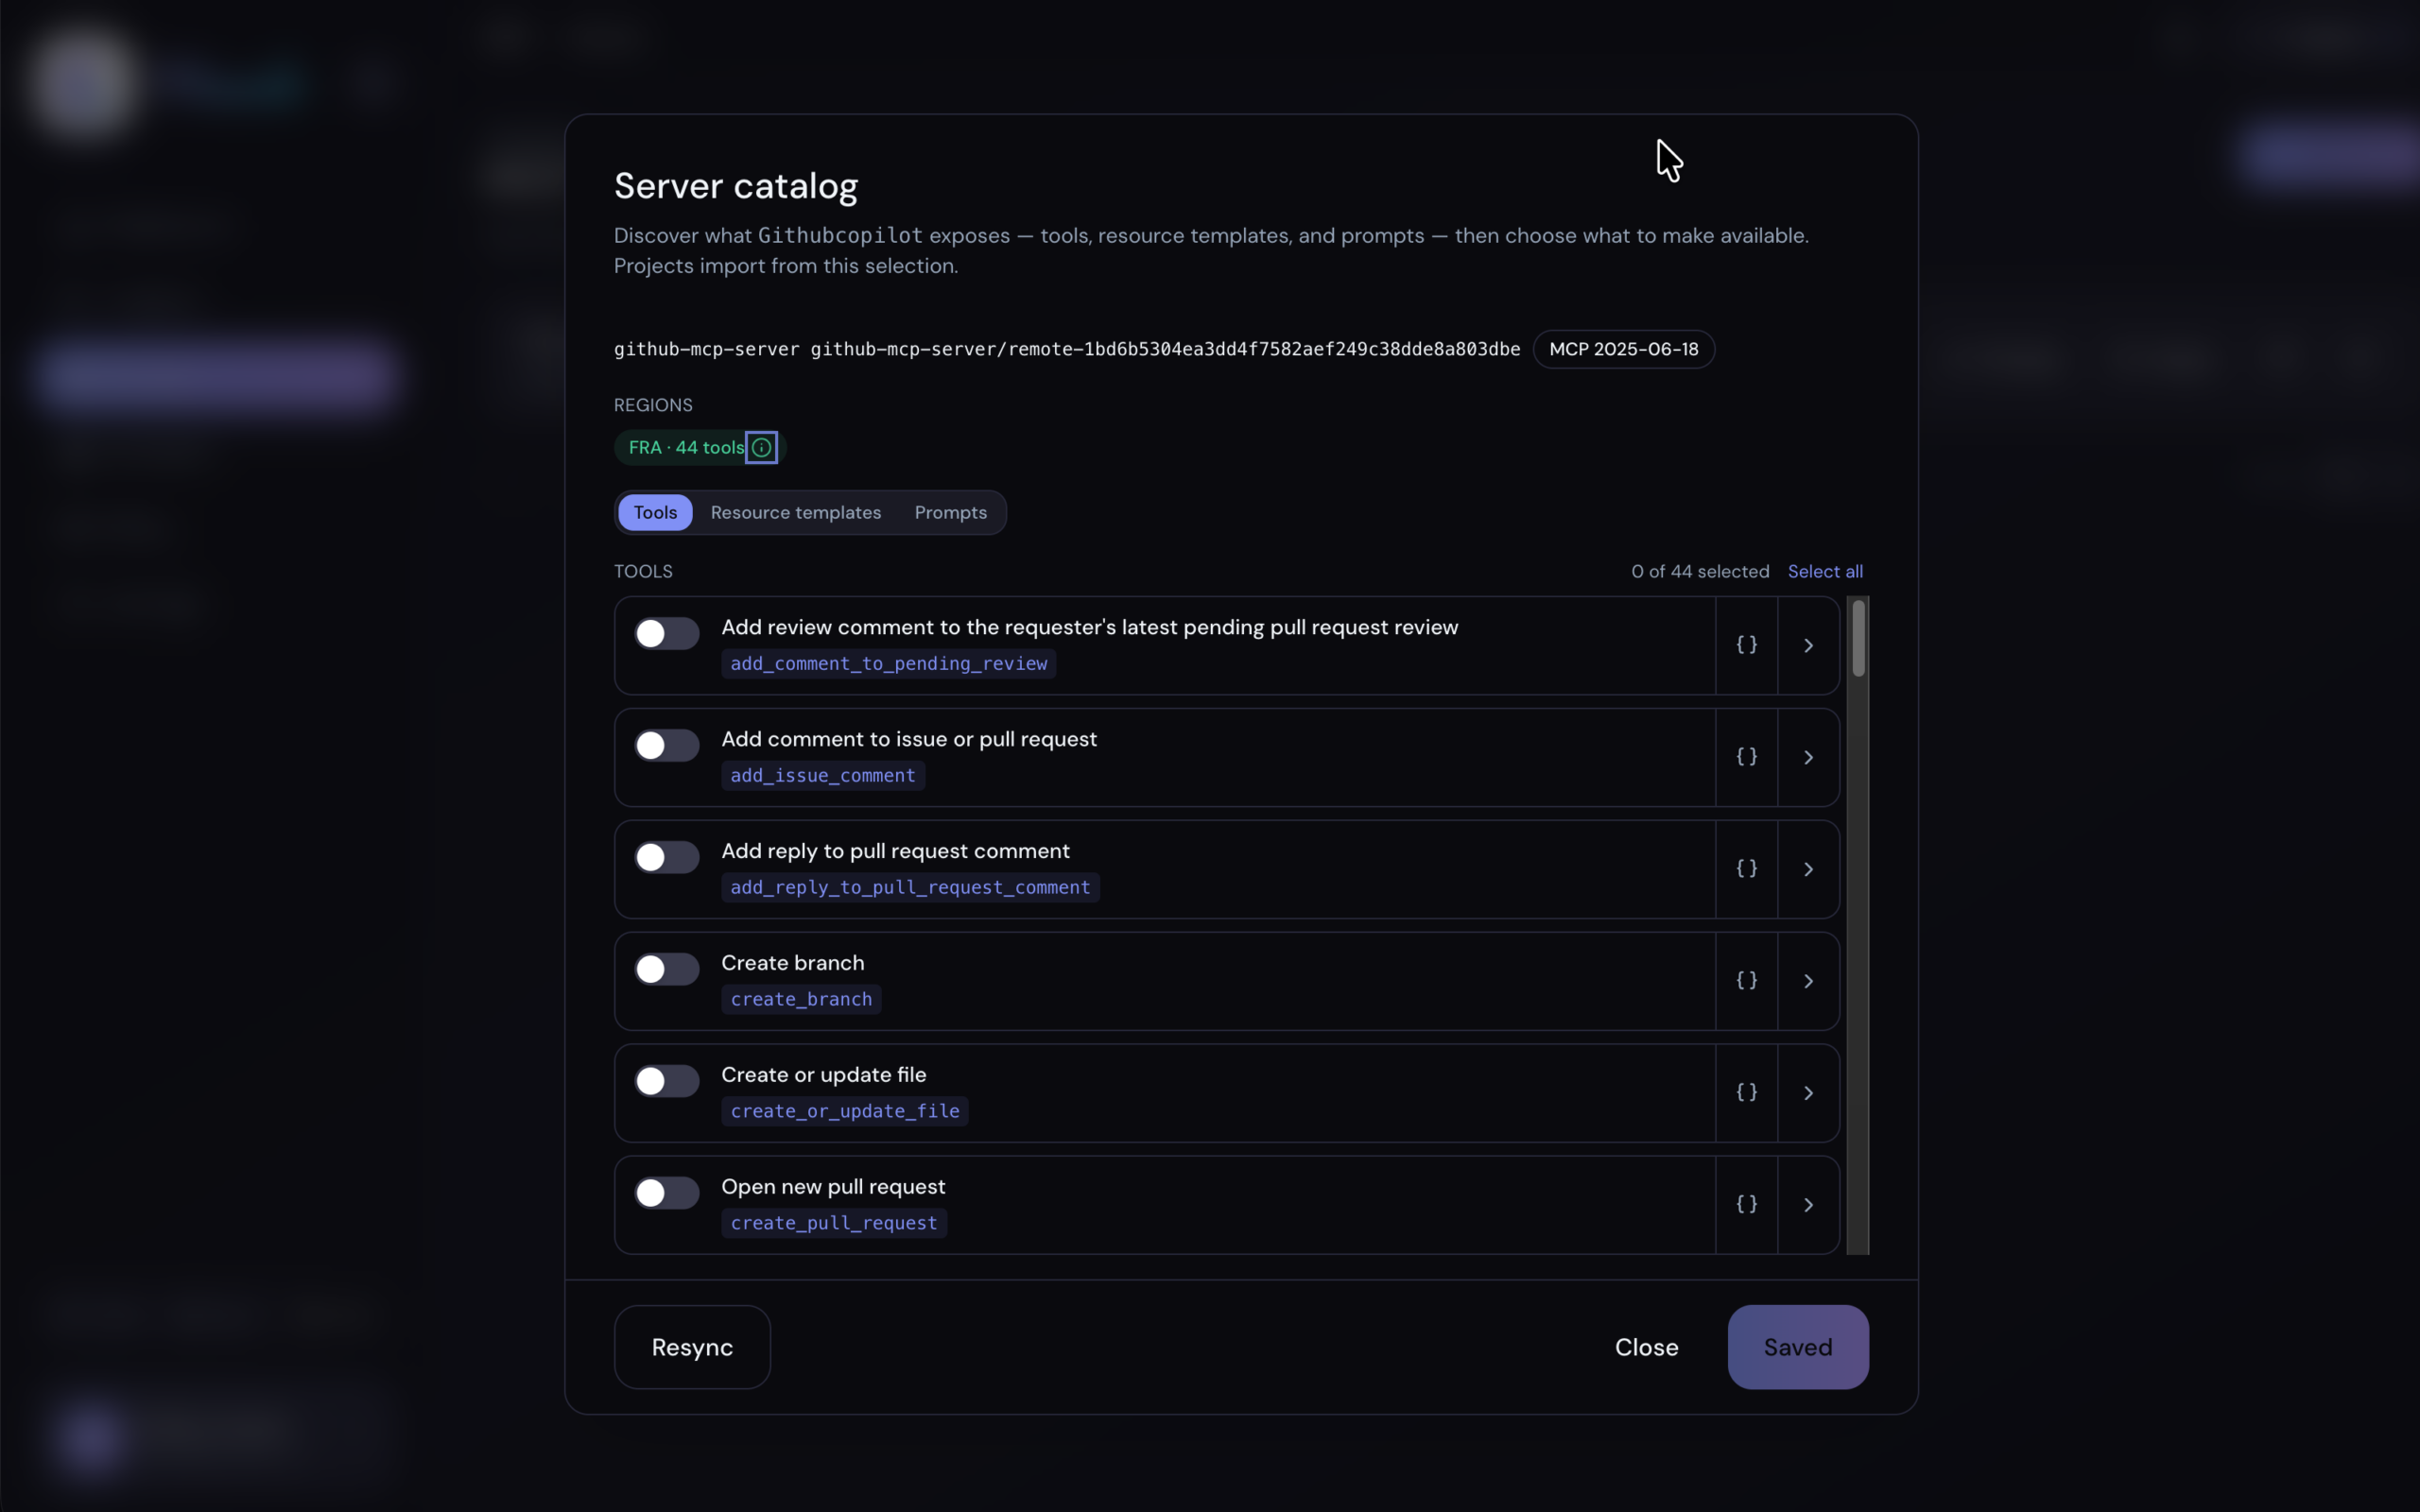
Curate
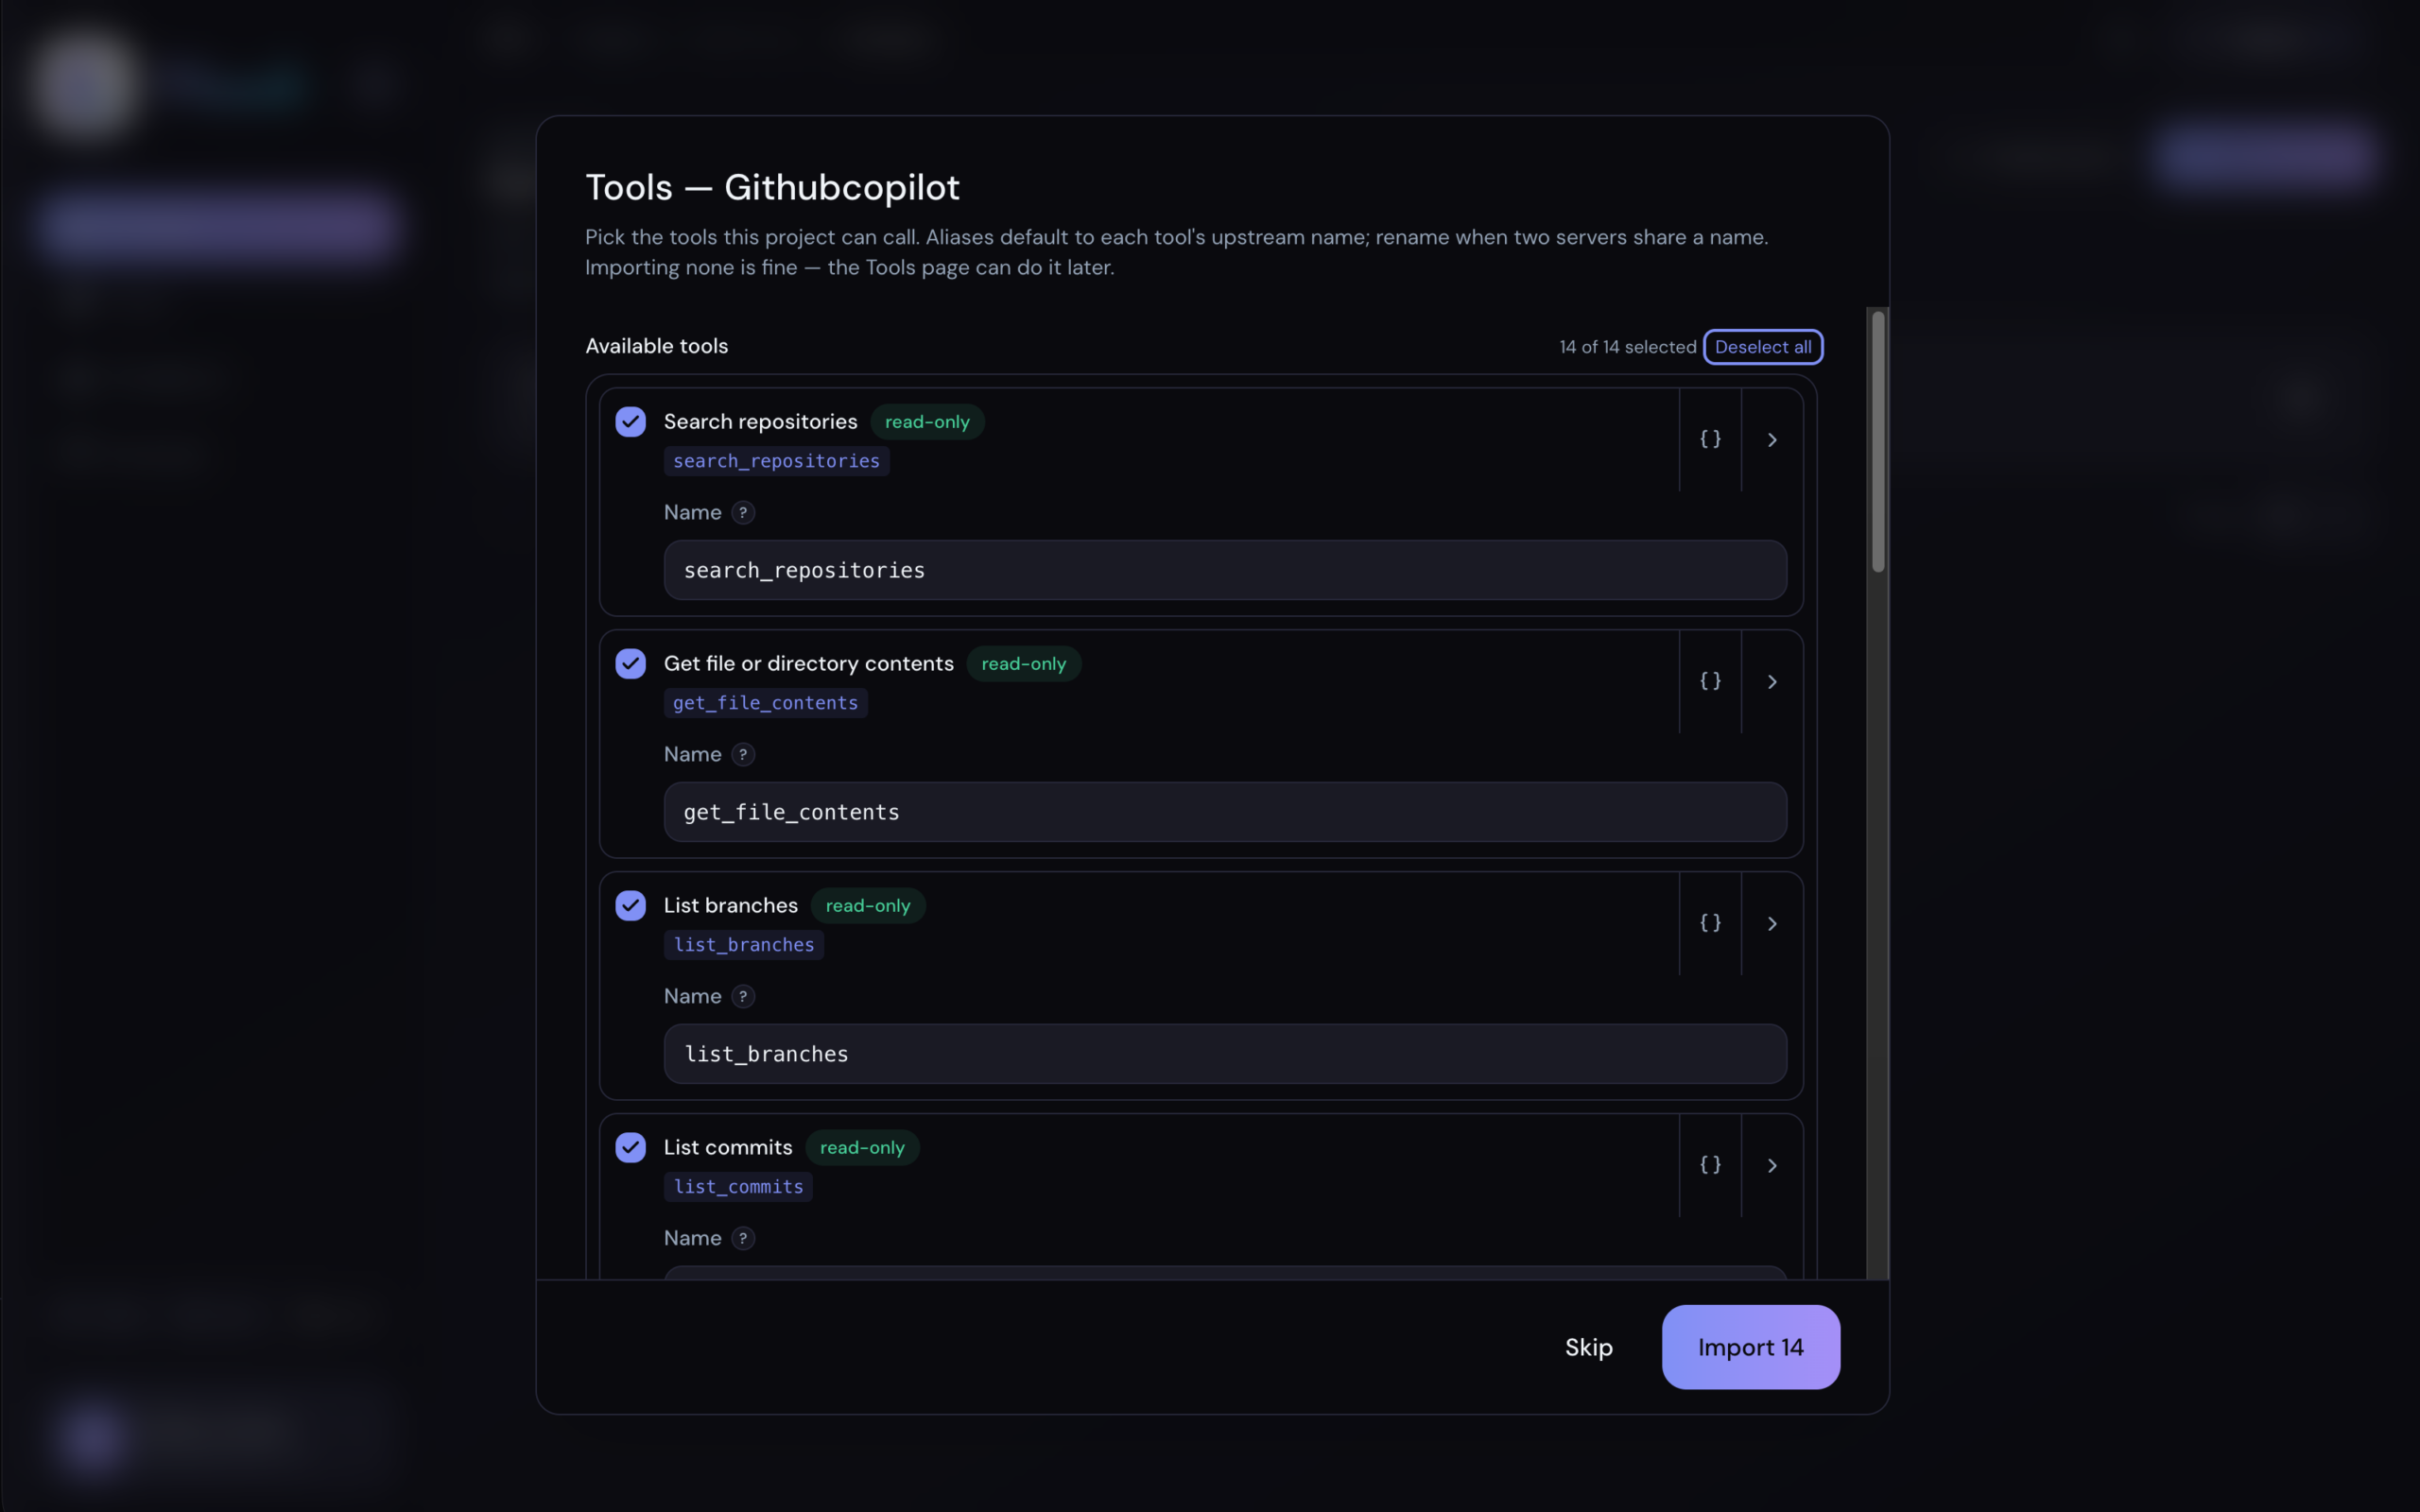
Pick the tools.
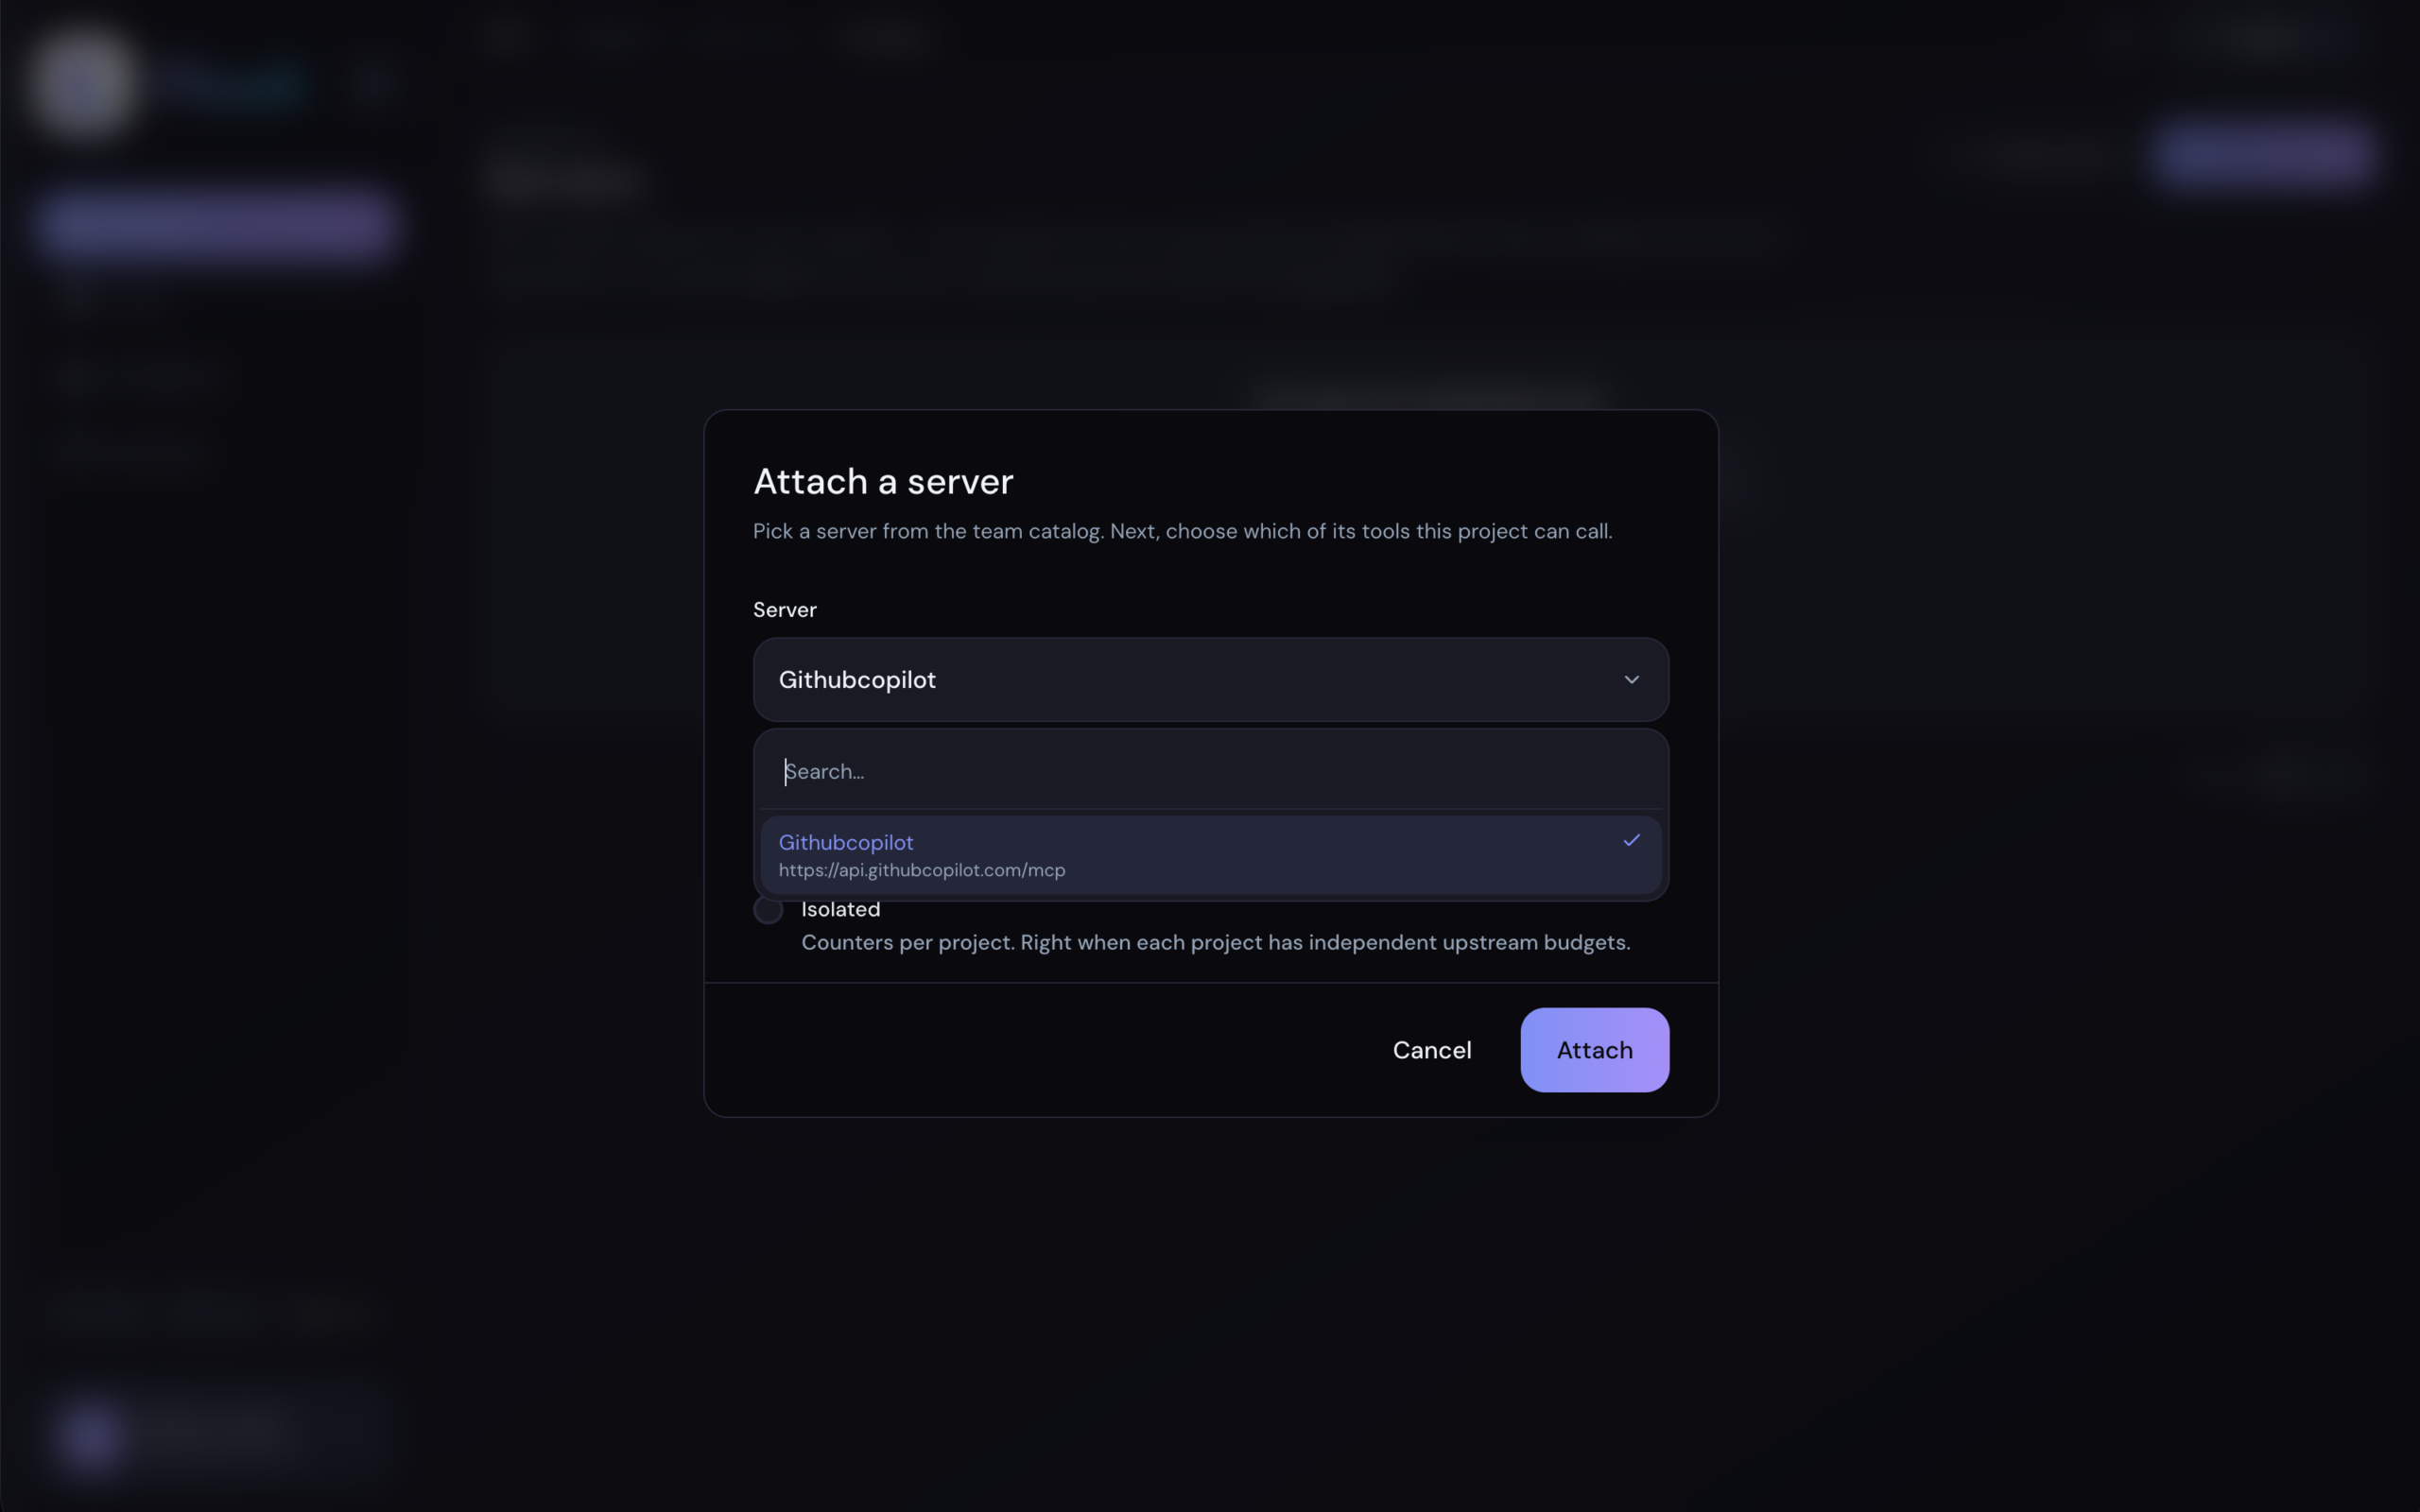
Two gates. The server's catalog opens as soon as it's added: tools, resource templates and prompts, each with a switch — that's what the team allows at all. Then, when a project attaches the server, it picks which of those tools it can call. Nothing reaches an agent unless it cleared both.
No URL, because you run the server yourself? That is a stdio MCP server, and Meandr supports those through the Meandr CLI. Connect a stdio server
Bring your servers however they sign in.
API keys, custom headers, basic auth, OAuth, mTLS or AWS SigV4 — Meandr adapts to the server, not the other way around.
API keys and basic auth
The two most common ways a tool server signs in. Give Meandr the credential once and it's attached to every request for you.
AWS SigV4, out of the box
AWS-hosted MCP servers expect AWS SigV4-signed requests. Meandr signs them for you on every call — no proxy or sidecar for you to stand up.
Encrypted, and revocable
Credentials are stored encrypted and never handed to an agent. Agents only ever hold a Meandr token — revoke it in one click.
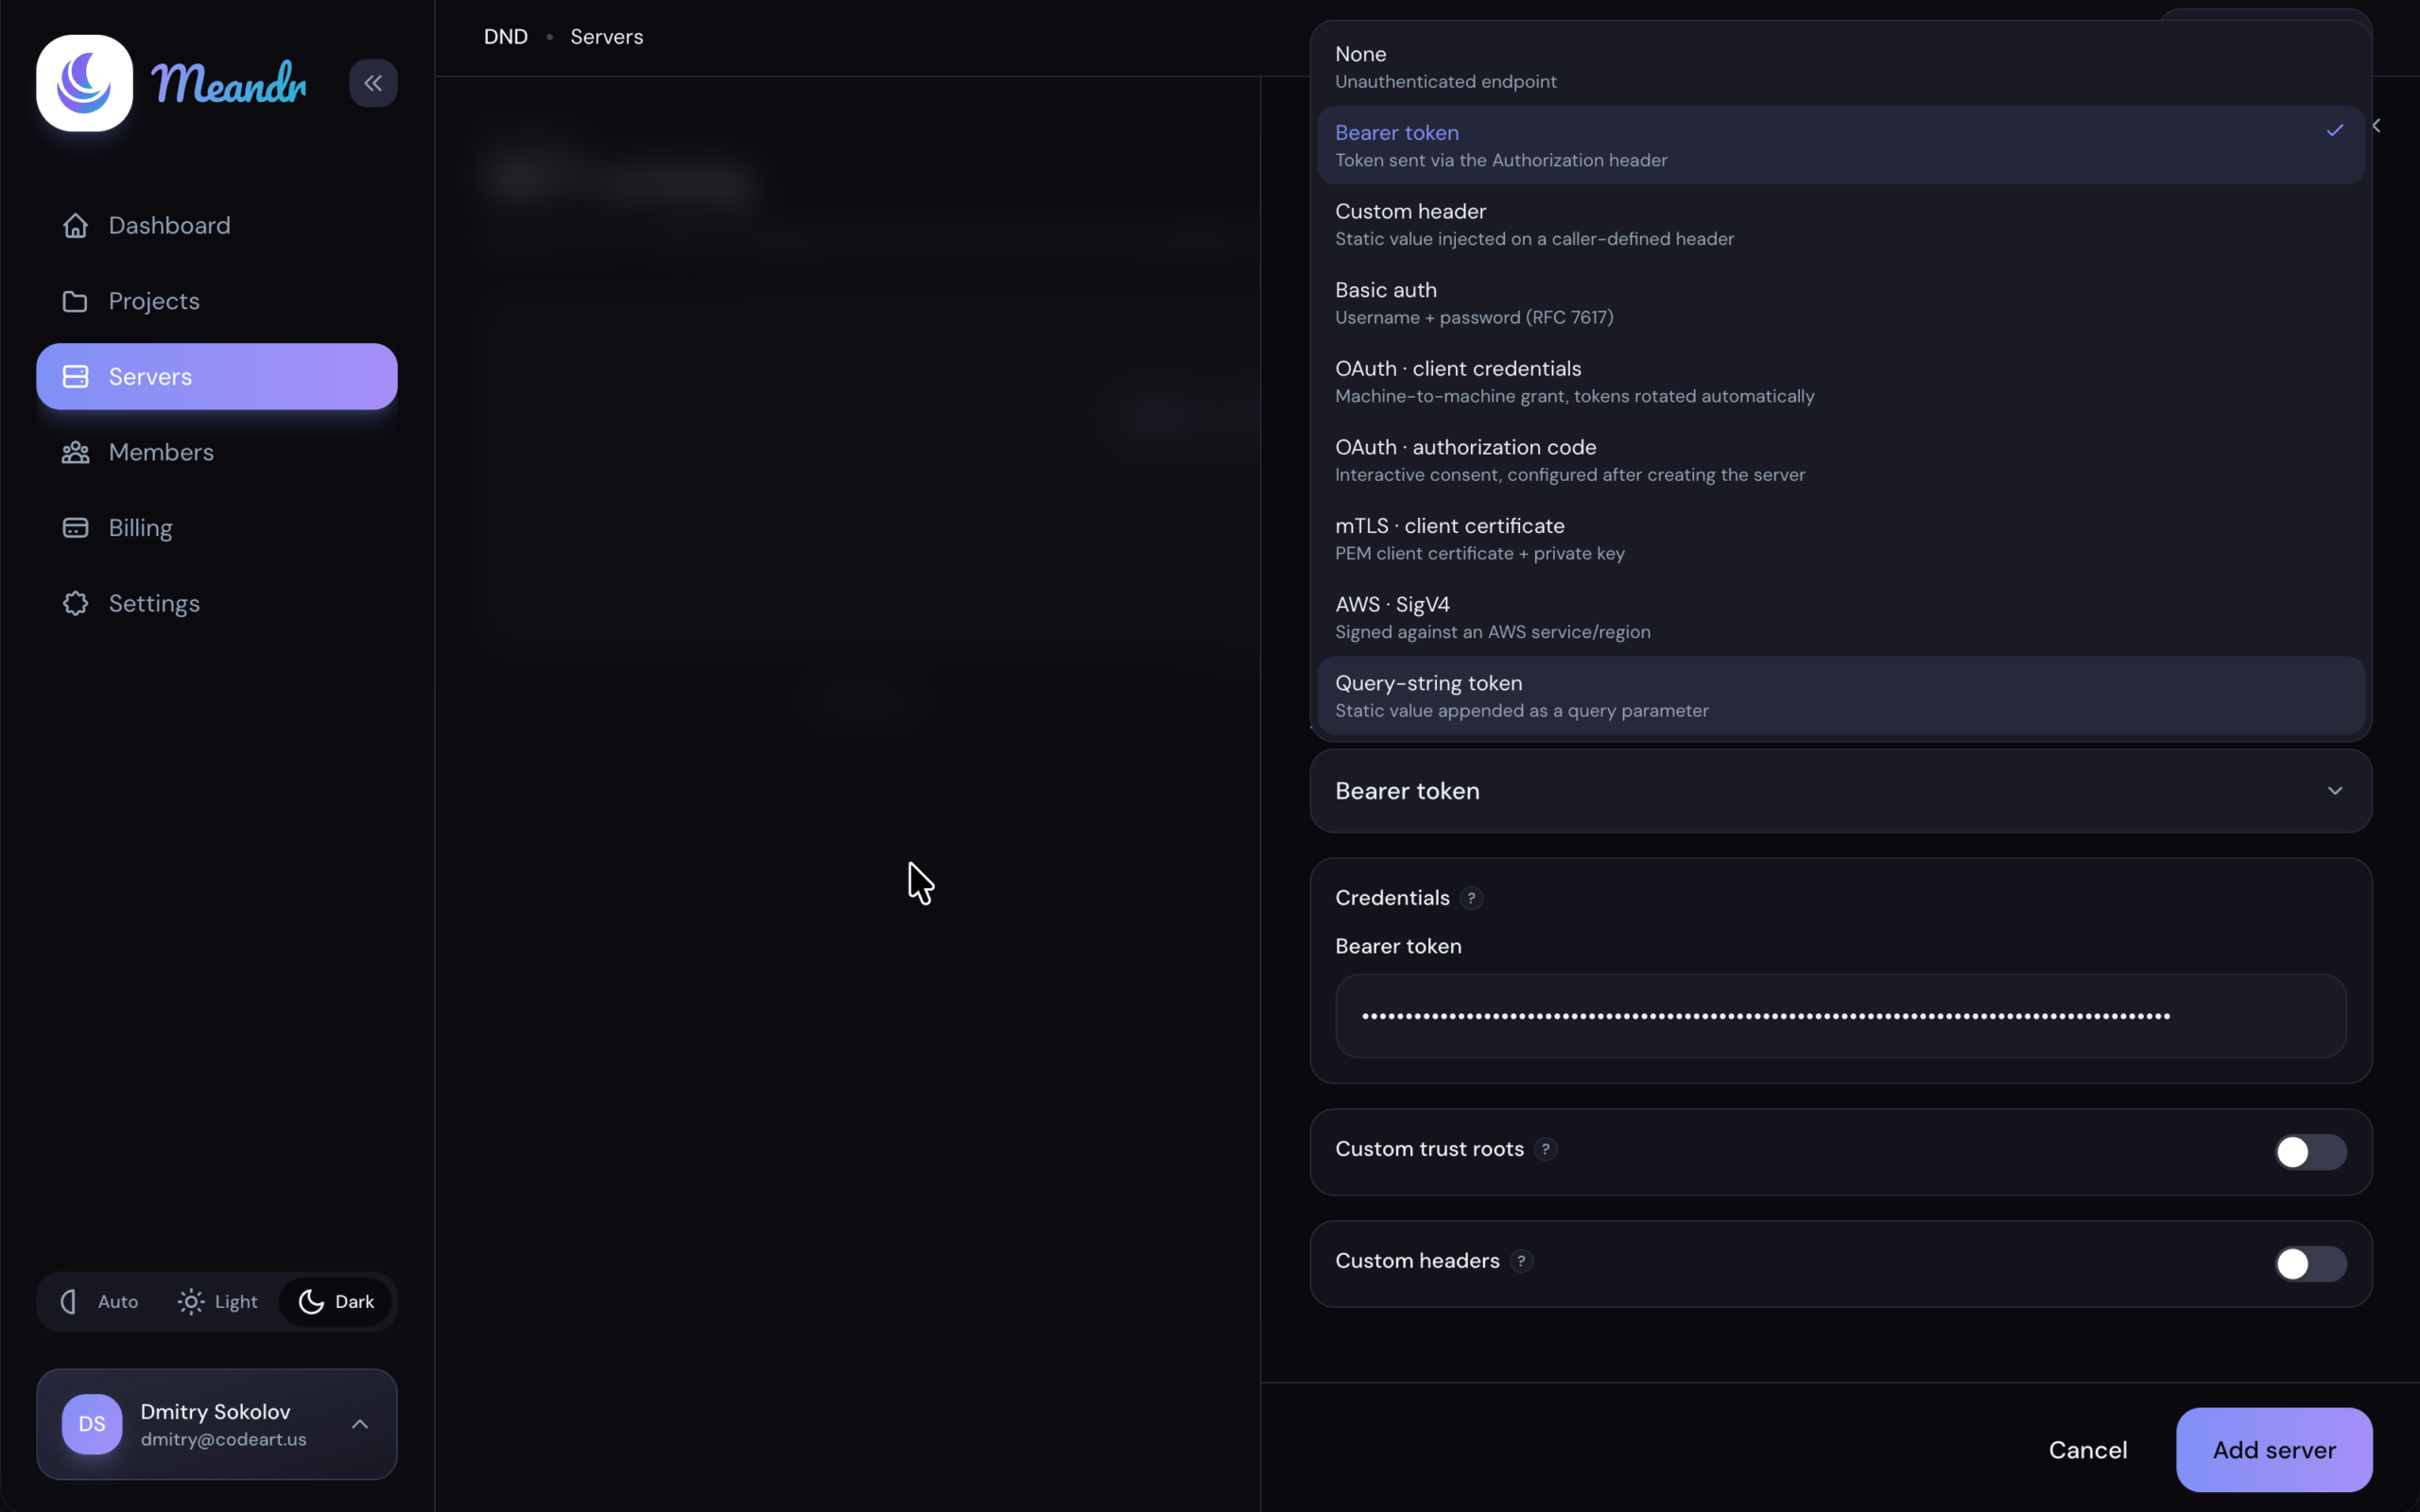
Supported Authentication Methods
| Auth method | What you provide |
|---|---|
| None | Nothing — the endpoint is open |
| Bearer token | The token — sent in the Authorization header |
| Custom header | A header name and its value |
| Basic auth | Username and password |
| OAuth · client credentials | Client ID and secret — tokens rotate automatically |
| OAuth · authorization code | Client details, then an interactive consent step |
| mTLS · client certificate | PEM client certificate and private key |
| AWS SigV4 | AWS credentials, plus the service and region to sign against |
| Query-string token | A parameter name and its value |
Next steps
Quickstart
Connect your first agent to Meandr — one URL and a token, no SDK.
Your first policy
Decide what your agents may do — allow, deny, or require a human's approval.
Connect a server, curate its tools.
Point your agent at one endpoint and you're governed in minutes — no code changes, no proxy to run.
Get startedQuestions? Email us