Solutions
Connect AWS MCP — no proxy required.
AWS-hosted MCP servers expect AWS SigV4-signed requests. Meandr signs them for you, so you point it at the server and it just works — no proxy or sidecar for you to stand up and babysit.
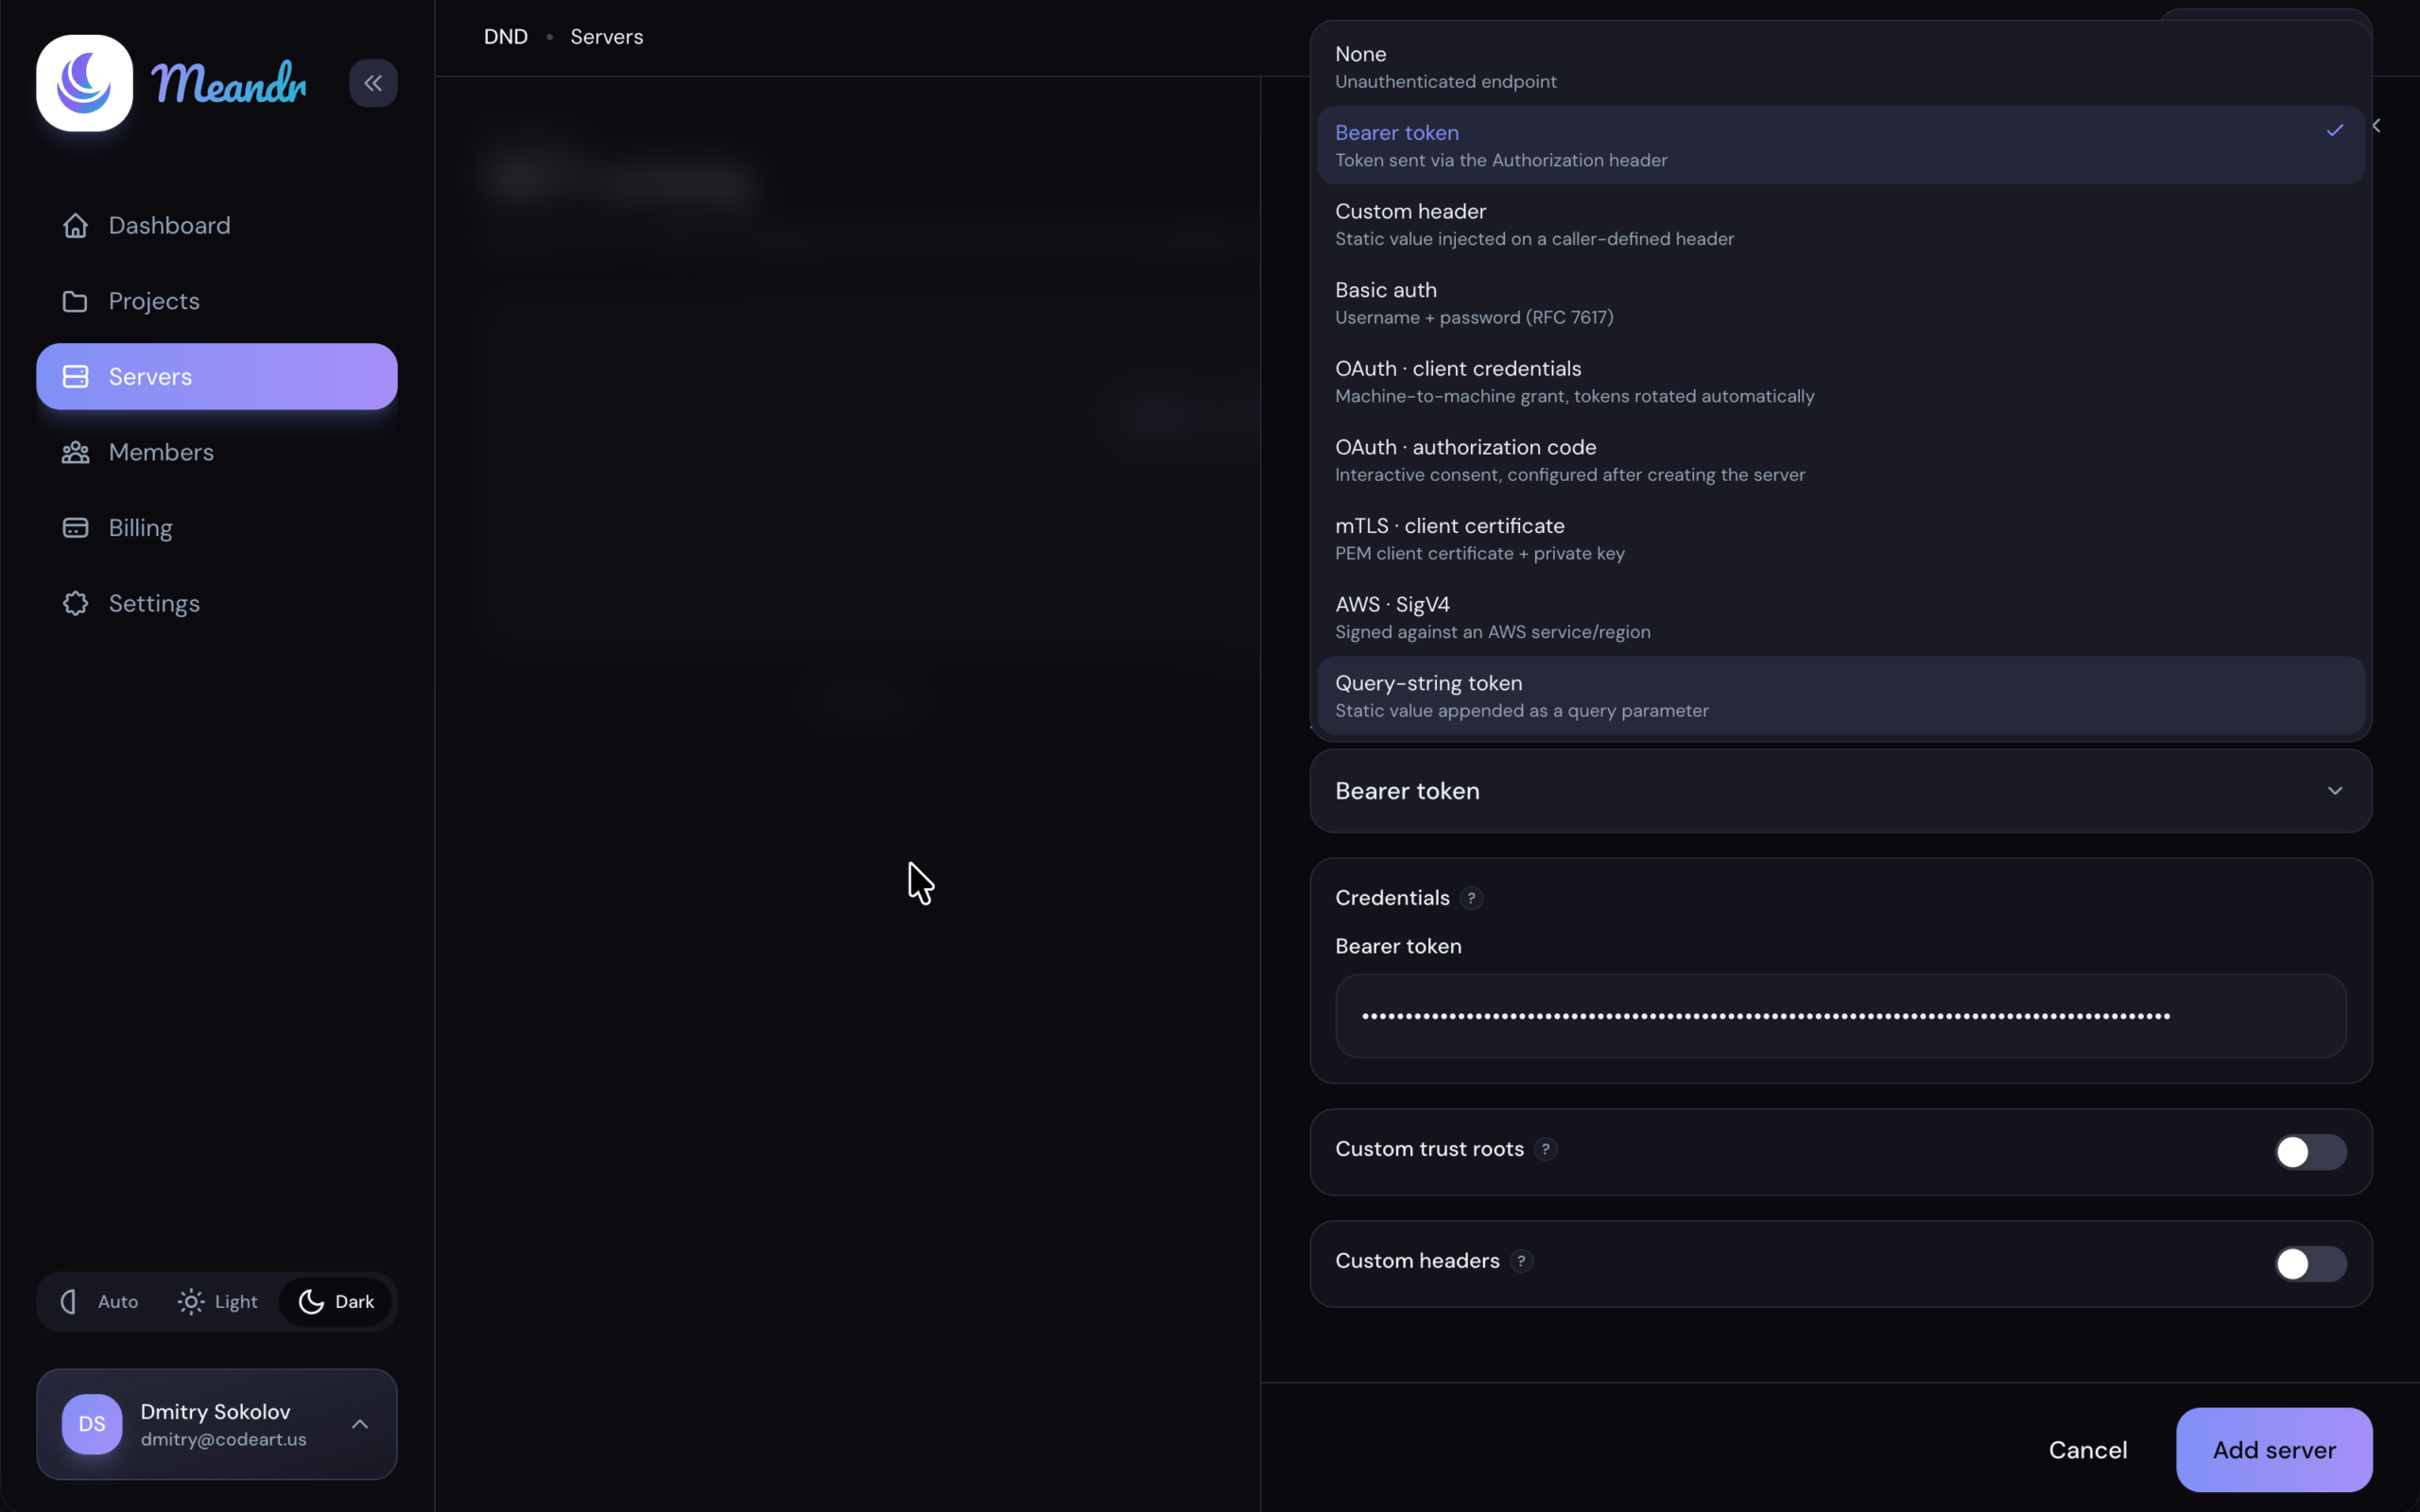
Add an AWS server like any other.
Paste the server's address and Meandr handles the AWS SigV4 signing behind it — there's nothing extra to stand up, and no proxy to keep alive.
AWS MCP servers don't take a plain token.
Getting a request in front of an AWS-hosted server takes more than a bearer token — and doing it yourself usually means running something extra.
AWS SigV4, not a bearer token
AWS MCP servers require AWS SigV4-signed requests. A plain API key or bearer token won't get you in — every request needs a valid signature.
Another sidecar to run
The usual workaround is standing up a local proxy just to sign requests — one more process to deploy, patch, and keep alive alongside everything else.
Easy to get wrong by hand
Building the canonical request, wiring up credentials, and getting the region right is fiddly — and a small mistake just fails silently as a rejected request.
How it works
Add the server. Meandr signs. Done.
The signing happens on Meandr's side, on every request — your agents never see it and never need to know it's there.
Add the server
Credentials and region.
Give Meandr the AWS credentials and region for the server, once. Meandr holds them encrypted — your agents never see them.
You set up: AWS credentials and region, in the dashboard.
Meandr signs
On every request.
Meandr builds the AWS SigV4 signature for every upstream request to that server, on the fly. Nothing to run yourself, nothing to keep patched.
You set up: nothing more — signing is automatic.
Just another server
Governed like the rest.
The AWS MCP server joins your catalog and is governed like any other — the same policies, rate limits, and audit trail apply.
You set up: policies and limits — same as any other server.
Questions you'd ask anyway.
What do I need to connect an AWS MCP server?
Do I need to run a proxy or sidecar myself?
Does this actually work today, or is it planned?
Can I mix AWS and non-AWS servers?
Connect your AWS MCP server without touching a proxy.
Point your agent at one endpoint and you're governed in minutes — no code changes, no proxy to run.
Get startedQuestions? Email us